Observability your security team will say yes to.
Scout runs inside your cloud, so your telemetry never leaves your boundary. ISO 27001 certified, SOC 2 Type II audited, with security reviews completed in under two weeks.
Your telemetry is sensitive data.
Logs, traces and prompts now carry customer data, business logic and regulated information. Sending them to a third-party cloud creates risk your security, legal and compliance teams have to answer for.
Regulators mandate where your data lives
Residency and localization rules now cover observability data too, so where your telemetry is stored needs to be documented and approved.
- Region-specific storage
- Cross-border transfer rules
- Audit-ready data location
Telemetry contains customer data
Logs include user IDs, traces include payloads, and LLM monitoring includes prompts. Keeping it compliant outside your cloud means constant redaction.
- PII in logs and traces
- Prompts in AI monitoring
- Redaction pipelines to maintain
Every SaaS tool needs security sign-off
A tool that stores your telemetry is a data processor, which means risk assessments, DPAs and a review cycle before rollout.
- Vendor risk assessments
- Data processing agreements
- Longer time to rollout
Scout BYOC answers the question of where your data goes: nowhere. The next question is whether you can trust what runs inside your boundary.
Keeping data in your cloud is half the answer. Proving it is the other half.
Security and compliance teams don't approve promises. They approve evidence: certifications, audit trails and an architecture they can inspect. Scout is built to give them all three, so approval takes weeks instead of quarters.
Independently audited
base14 is ISO 27001 certified and SOC 2 Type II audited, with independent penetration testing at least once a year. Scout BYOC deployments come with security documentation ready for your vendor assessment, and review support that typically wraps up in under two weeks.
- ISO 27001 certified
- SOC 2 Type II
- Annual third-party penetration testing
- Assessment-ready documentation


Designed so your data never has to leave
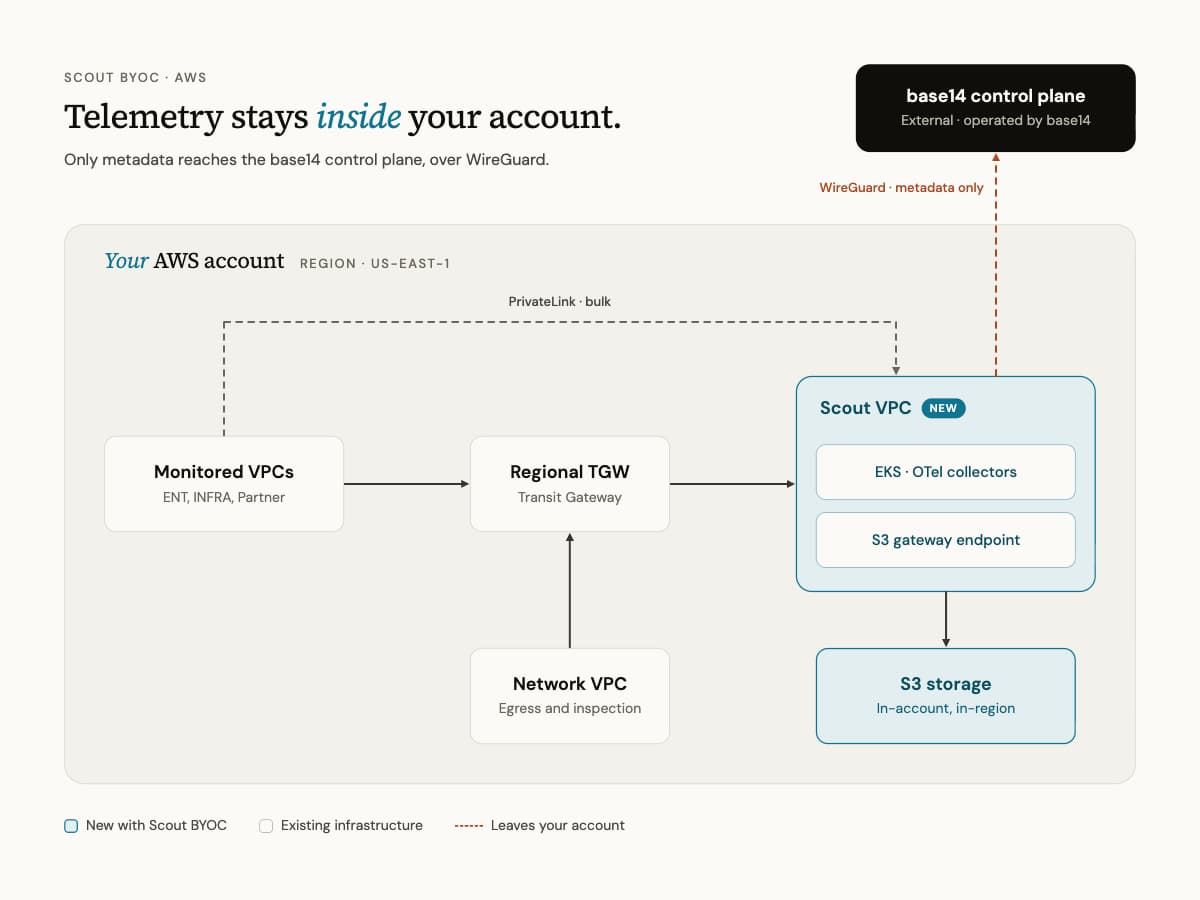
Your cloud, your data
The collector, OpenTelemetry gateway and telemetry datalake all run inside your VPC. Telemetry is stored and queried in your account.
Open standards, no black boxes
Scout is OpenTelemetry native with no proprietary agents, so your team can inspect exactly what is collected and where it goes.
Access you control
Role-based access, audit trails, TLS 1.3 encryption in transit, and retention policies you set.
Redact what you choose. Keep what you need.
Sensitive data should still be redacted. With Scout BYOC, your team decides how. Redaction runs in your own OpenTelemetry collector, under your policies, so you can protect what matters without losing the context you need to debug.
Redaction rules you set
Decide what's masked, dropped or kept in your logs and traces, based on your own policies rather than a vendor's defaults.
AI monitoring, your way
Choose whether prompts and responses are masked or kept for debugging. Either way, they're stored in your cloud.
Query detail where it's allowed
Keep query text and parameters where your policies permit, and mask them where they don't, when chasing slow queries and lock contention.
Metrics, logs, traces, PostgreSQL, Kubernetes and LLM monitoring, all correlated in one platform. OpenTelemetry native, deployed with a Helm chart in under 2 hours.
Explore ScoutYour region. Your cloud. Your timeline.
Your residency requirements decide where Scout runs, not the other way round. Wherever your data has to stay, we deploy inside the region your regulators and customers require.
Ready to take Scout through your security review?
Drop your email - we'll set up a walkthrough.